Sunday, 11 October 2026

 ngraham
Welcome to the latest edition of This Quarter in KDE Digital Sovereignty!
This blog series covers the work done throughout KDE’s software stack that’s funded by the investment KDE received earlier this year from Germany’s Sovereign Tech Agency.
Commissioned work on a variety of projects has been done by KDE contributors working for KDE e.V. itself, as well as the Techpaladin Software, enioka Haute Couture, and MachineSoul companies.
This post will cover the work done in the third quarter (Q3) of 2026. Let’s get into it!
Quality assurance and testing
QA work continued in Q3, this time largely to polish and improve upon the work that was landed in Q2.
On the KDE Linux side, the OpenQA system received a lot of work both to maintain it, and also to reduce ongoing future maintenance needs, as well as adding more tests. Some highlights include:
- Verifying bootability of the prior build after an upgrade
- Verifying that secret service credentials are preserved after an upgrade
- Testing Btrfs snapshotting facilities
On the PIM side, the end-to-end tests continue to pay dividends. Lots of effort went into fixing the issues they uncovered. This included issues like:
- CalDAV handling of recurrence exceptions
- KOrganizer missing some recurrence exceptions
- Parsing custom properties in CalDAV
- Broken foreign keys cascading when Akonadi server uses sqlite as backend
- Unwanted iTIP sequence incrementation when accepting invitations
This allowed us to remove all the expected fail marks which were still present on some of the tests.
With this QA safety net in place, we’ve been working on landing long-needed improvements around DAV support. For instance, it’s been migrated away from KIO to use QNetworkAccessManager leading to a large performance boost. Further performance enhancement is expected from the work to port the DAV Akonadi resource to ObserverV3 allowing batching of some operations.
IMAP4rev2 and WebDAV-Push
The work on QRESYNC support in the IMAP Akonadi resource has been completed, providing a very nice boost to email syncing by making it faster, and drastically reducing the network bandwidth used for a sync. This pretty much concluded the work on the IMAP4rev2 upgrade of our stack.
Focus then shifted to WebDAV-Push support for DAV Akonadi resources. More of the protocol is getting implemented like support of the “Don’t Notify” header to avoid getting notified of our own changes. The DavPush notification subscription code path has also been completed.
This allows us to move to the next step which is integration of the various components involved and the addition of new end-to-end tests to validate the whole chain.
An interesting side effect of this work has been the need to implement support for DAV sync-tokens, which is supported by most servers. This will simplify calendar syncs even if your server doesn’t support WebDAV-Push. We expect it to improve the syncing of calendars in a similar way to the improvements with emails we’ve experienced with QRESYNC.
This work is not completed yet, with a few merge requests still in flight. But expect next year’s release to fly for syncing IMAP and DAV.
Security
Plasma’s security infrastructure received a great deal of work in Q3. Much of it is non-flashy, but rather intended to shore up and modernize the foundations. As part of that work, Plasma’s lock screen gained a more flexible system that supports multiple authentication methods being configured and made available in different combinations:

Work is now ongoing to apply this feature to Plasma Login Manager, and share more security infrastructure between them.
Recoverability
Work began on adding a “safe mode” to Plasma, wherein you’ll be able to log into a dedicated troubleshooting environment that offers tools to help you get back to a working session.
This work is all in progress, with parts expected to start landing in Q4.
Network share handling
KDE’s network share handling improved in two significant ways in Q3. First, network FUSE mounts created by kio-fuse will now be automatically mounted if needed when you open a file that was previously accessed from a kio-fuse mount path. And those paths are now stable across logins, meaning that paths involving kio-fuse mounts also remain accessible across logins.
Work also began to remove blocking file access calls in KDE software, so that network shares accessed via mounts (FUSE or otherwise) are less likely to cause freezes and hangs — starting with Dolphin.
Data integrity
Q3 also saw a significant amount work on the topic of data integrity, from multiple angles.
First, the kio-snapshot service built in Q2 received a large amount of technical and user interface polish to make it a practical and reliable tool for users whose systems take Btrfs snapshots.
That tool was then integrated into KDE Linux, along with the Snapper Btrfs shapshotting system, thereby providing automatic user-level file snapshots by default. You can read a bit more about this in the August 2026 KDE Linux blog post.
The Baloo file indexing system was also made aware of Btrfs snapshots — specifically, how to not index them!
And because the concept of “free space” can be somewhat fuzzy on snapshotted filesystems, work is ongoing to surface information in more comprehensible ways, starting with KDE’s Filelight app.
Finally, the Kup backup system — which was previously released independently — was made a part of Plasma, so it will now see regular releases on the same schedule as Plasma itself. As a prerequisite to this, Kup was fully ported to Qt 6 and its widget received some more polish. Kup was also configured to avoid backing up large Flatpak apps and runtimes installed at the user level by default. And in the process, a longstanding bug afflicting multiple System Tray widgets was fixed.
Configuration management
The topic of strengthening KDE’s configuration management continued in Q3. First, even more apps and parts of Plasma were ported to use KConfigXT, and some had their settings refined to move volatile state data out of their configuration files.
Leveraging this expanded use of KConfigXT, the team created a GUI config editor app that offers system administrators the ability to graphically visualize and change configuration options. This app is still a work in progress, but shows the promise and potential of fully adopting schema-based configuration.
Account Autoconfig
On the PIM side, work to ease setup is moving towards exposing the new facilities to the user. Indeed, the KAccountAutoconfig library is almost feature-complete with one patch still to go through review.
Once it’s merged, we’ll start the process of moving the library to KDE Frameworks, and then begin integrating it into KOnlineAccounts and the individual PIM apps. We already have a prototype port of kmail-account-wizard to use this new library — a good first use of this library to prove it works properly.
Kontact Flatpak
Last but not least, work on the Kontact Flatpak integration with Plasma has started, and we’re currently scoping out requirements. The dependency chain between Plasma and the PIM stack will be completely reworked: it will be D-Bus based, and we’re working on defining the interfaces.
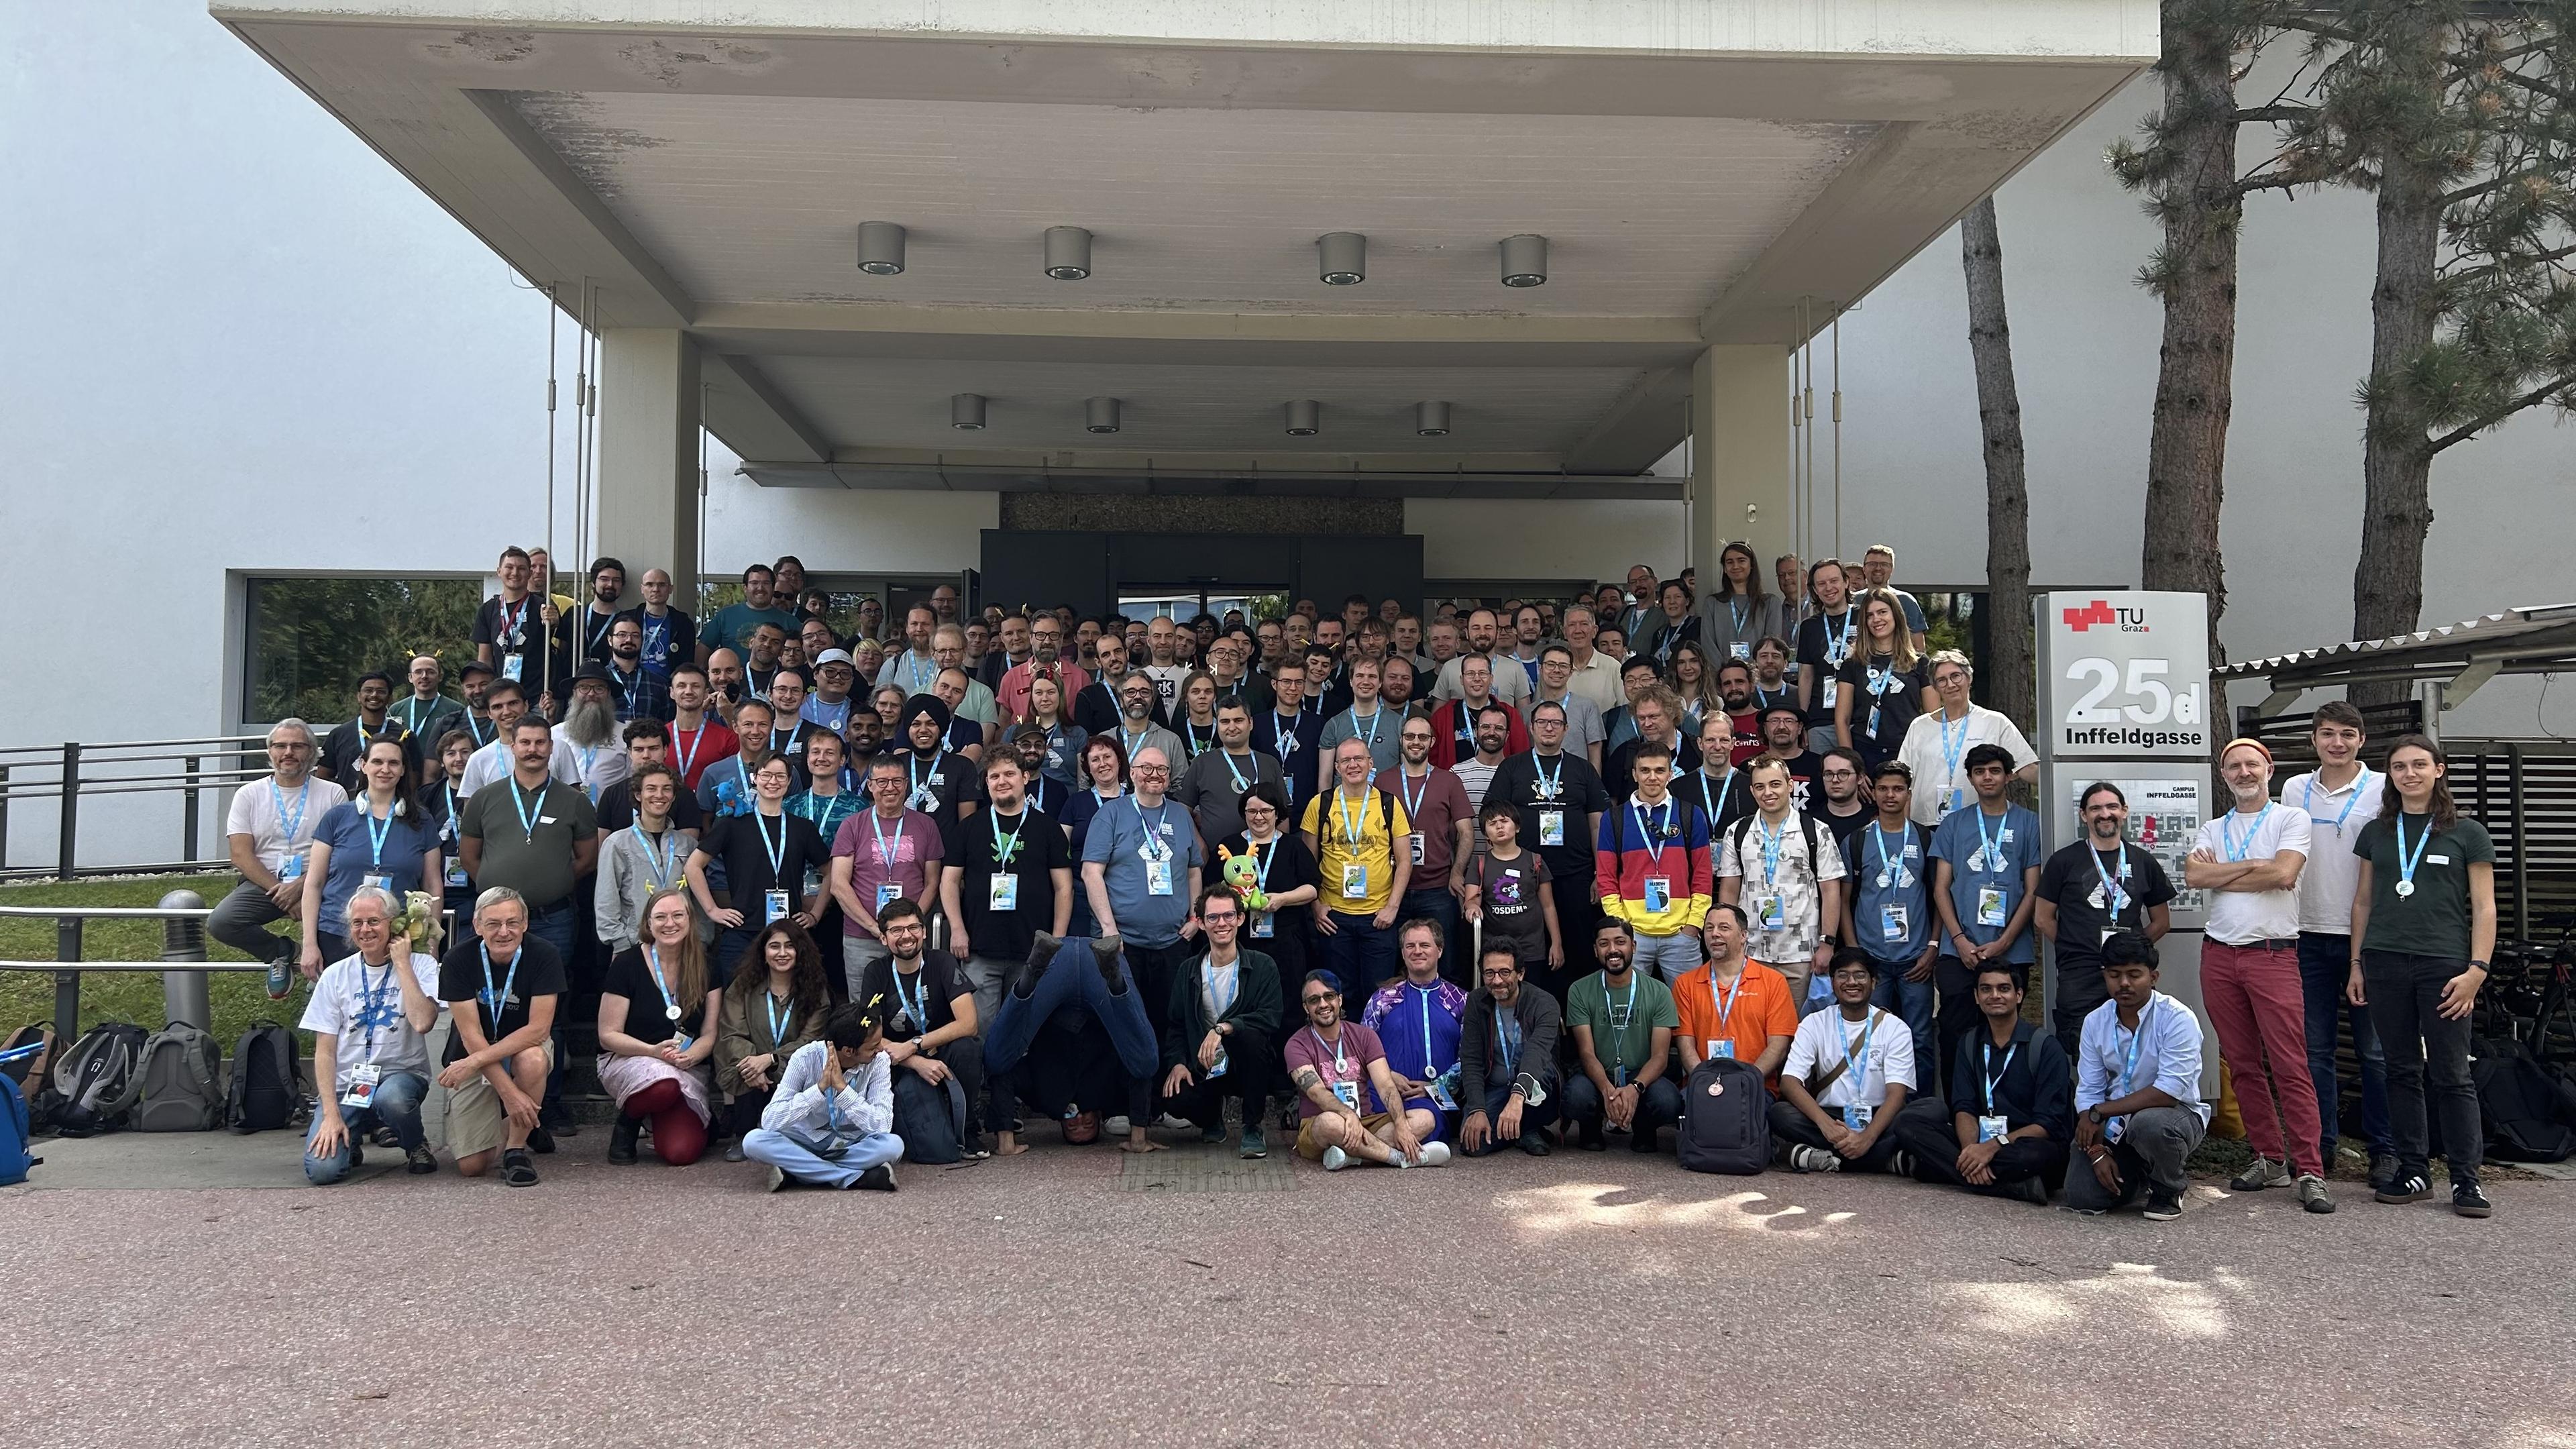
Attending Akademy 2026 definitely helped, as we got interesting input during the PIM BoF on the direction to take. This will lead to options which might benefit more contexts than the desktop, and so hopefully one day help Plasma Mobile as well.
Stay tuned for more details when the implementation work will be underway.
Looking forward
User-facing work has begun! We anticipate that this will continue in Q4 of 2026. And we’re very grateful for the Sovereign Tech Agency’s investment in KDE that made this possible!
 obiwan_kennedy